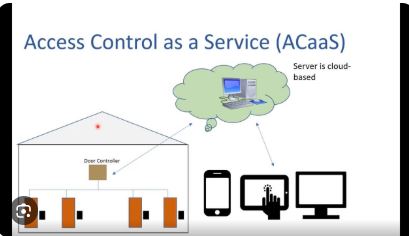
The migration from legacy on-premises physical access control systems to cloud-native platforms represents a massive paradigm shift in corporate infrastructure. Modern enterprise environments are moving away from dedicated on-site servers, proprietary local cabling, and localized administrative terminals toward centralized, API-driven architectures. This transition allows organizations to consolidate credential management, logging, and security automation across global facilities into unified operational dashboards. Centralized management dramatically reduces the friction of provisioning credentials for hybrid workforces, vendor technicians, and temporary visitors across geographically dispersed sites. Cloud platforms further enable automatic firmware updates, zero-trust network architectures, and dynamic risk scoring based on access logs. However, security architects must carefully evaluate latency issues, local survivability in the event of internet outages, and system compatibility with existing hardware. Modern edge controllers now feature local decision-making engines and offline caches to ensure seamless door operations even when cloud connectivity is temporarily disrupted. Organizations seeking comprehensive data on market performance, adoption trajectories, and industry benchmarks can explore detailed insights in the Access Control As A Service Market analysis.
From an operational standpoint, adopting cloud-native physical security eliminates the heavy capital expenditure associated with maintaining local server hardware, database licensing, and manual patch management across isolated sites. Internal IT and physical security teams no longer need to execute site visits for routine system upgrades or firmware patches, freeing up human resources for strategic threat hunting and risk mitigation. Furthermore, API integrations allow access control platforms to interface with enterprise identity providers like Okta or Azure Active Directory, ensuring immediate credential revocation when employees depart. This cross-domain synchronization eliminates dangerous windows of vulnerability where separated personnel retain physical door access due to administrative delays. Nevertheless, hardware migration remains a complex undertaking; replacing legacy door controllers, card readers, and wiring runs often requires phased hybrid deployments. Security teams must establish robust governance frameworks to balance cloud scalability with localized hardware reliability during transitional periods.
Discussion Questions
-
How can multi-site enterprises maintain local physical survivability at door controllers during prolonged internet outages without forfeiting centralized cloud monitoring?
-
What are the most effective strategies for harmonizing cloud identity providers with legacy physical access hardware during a phased infrastructure migration?
➤➤➤Explore MRFR’s Related Ongoing Coverage In Semiconductor Industry:
South Korea Microinsurance Market
South America Microinsurance Market